Managed collaboration
Auditors, consultants and internal teams share one platform instead of email exchanges. Documents, approvals, deadlines and activity history are in one place, and evidence is collected automatically from connected data sources.
Compliance under control: NIS2, ISO, DORA, GDPR and other regulations
Conclusion Audit and compliance module – Eller Compliance Hub – takes you from regulatory obligations to continuously managed, demonstrable compliance. NIS2, ISO/IEC 27001, DORA, GDPR and other regulatory frameworks are managed in one place, with an audit trail and full control.
Save weeks of manual work and the stress of meeting regulatory requirements. Instead of scattered evidence, manual chasing and an unclear change history, auditors, consultants and internal teams work in one shared record – with deadlines under control and a traceable audit trail.
Go beyond a one-off assessment of your obligations to lasting confidence in compliance. Requirements, risks, controls and evidence stay up to date, and you can demonstrate the state of compliance at any time – to leaders and to regulators.
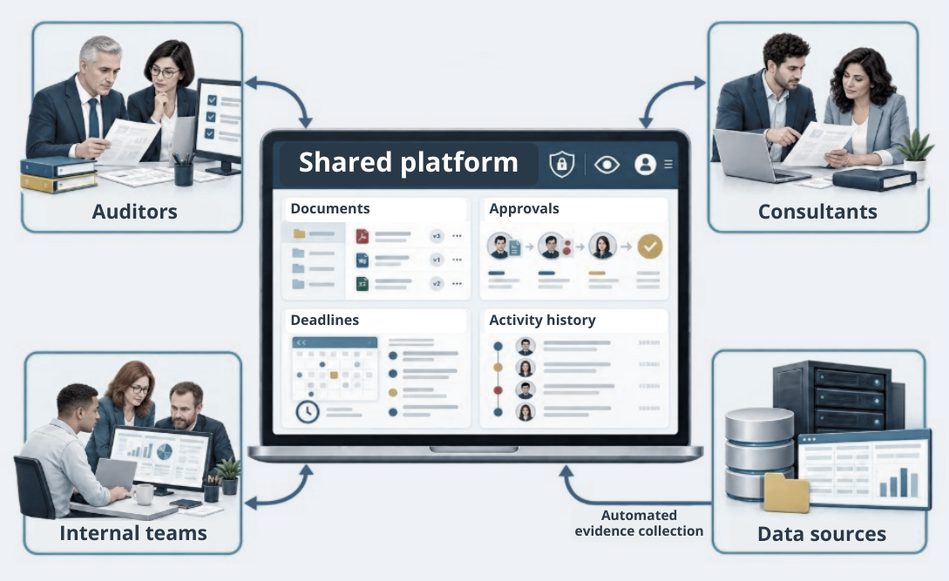
Auditors, consultants and internal teams share one platform instead of email exchanges. Documents, approvals, deadlines and activity history are in one place, and evidence is collected automatically from connected data sources.
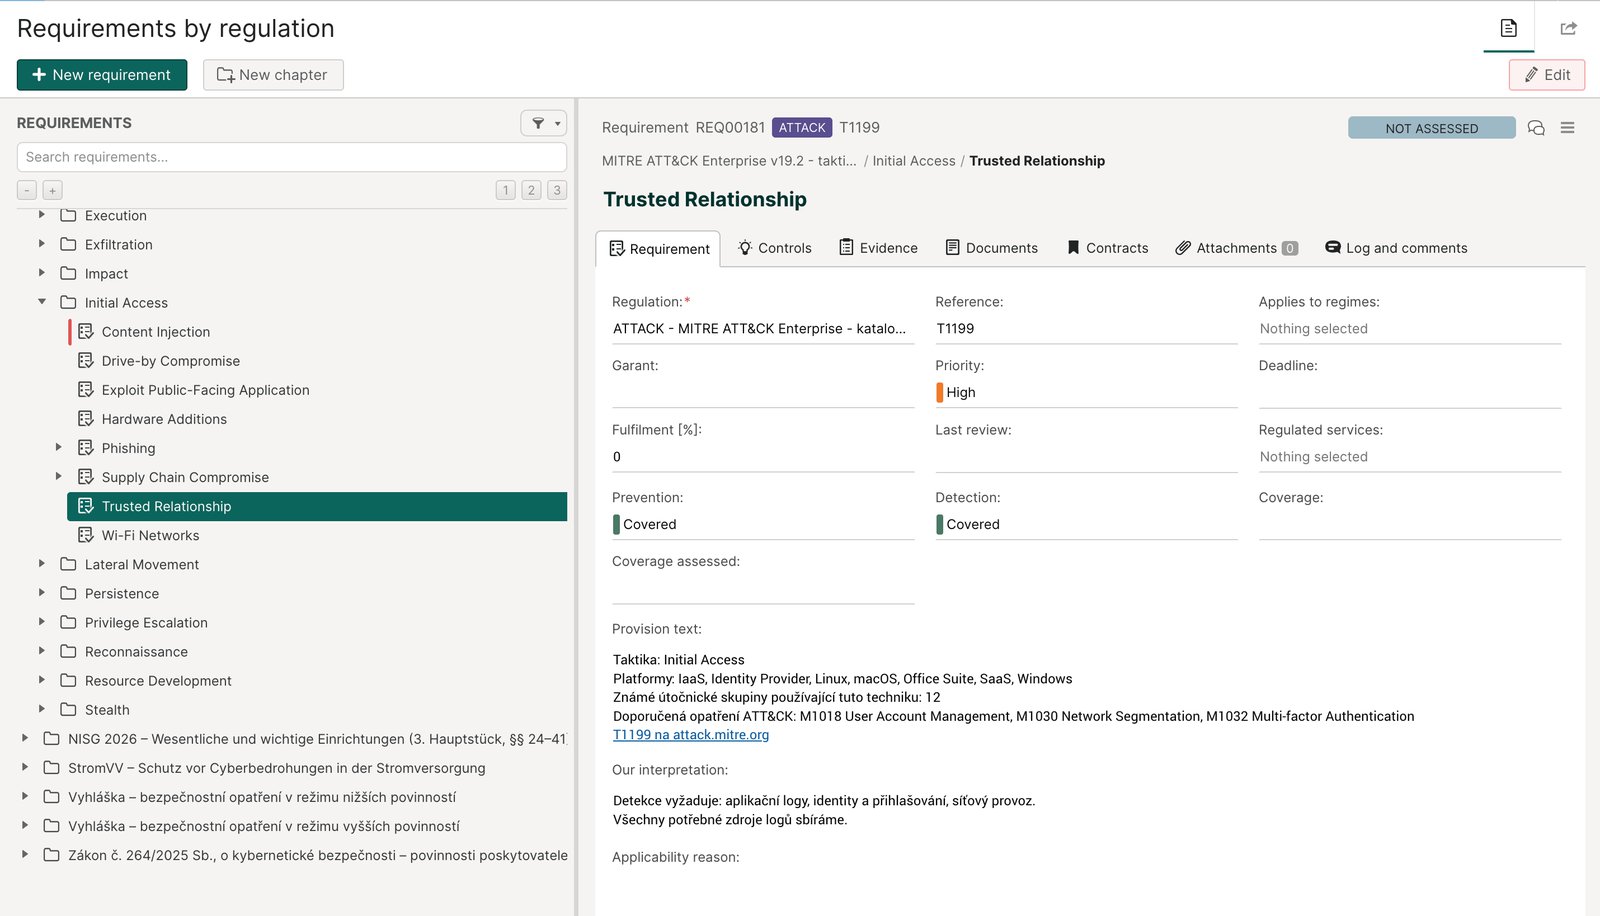
All regulations and frameworks in one structured catalogue – national NIS2 laws, ISO/IEC 27001:2022 Annex A, DORA, GDPR or MITRE ATT&CK. Each requirement has its owner, priority, deadline, applicable regimes, regulated services and date of the last review, with controls, evidence and documents attached.
Manage regulatory requirements, responsibilities, controls and evidence in one place, with support for practical implementation. Controls are mapped across regulatory frameworks, so one control can demonstrate compliance with several of them.
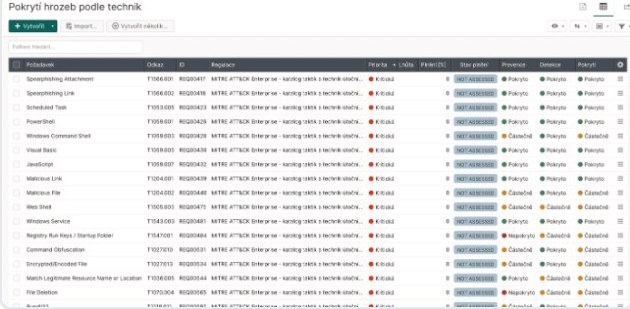
See which threats and attack techniques are covered by your controls, mapped to MITRE ATT&CK. Prevention, detection and coverage are assessed for each technique, so gaps are visible before an audit finds them.
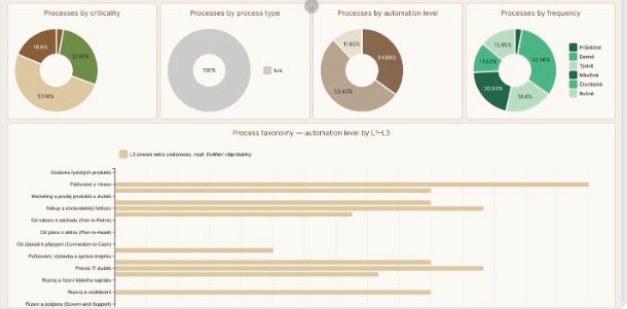
Report compliance status to leaders and regulators. Dashboards, exports and a complete audit trail are generated from live data – no manual collection of evidence before an audit.
Saves specialists and teams time with proven processes and consolidated data in one place, replacing manual searches
A preconfigured solution significantly reduces implementation time – requirements, controls and workflows are ready to use
Roles, permissions, versioning, audit trails and verifiable evidence. Host data on your premises or in the EU (SaaS)
Single sign-on, Active Directory and LDAP, workflows and alerts, integration with your existing systems
Connect asset registers, policy repositories, training and logs to your systems, or manage them directly in the platform. Add further regulatory frameworks without introducing another tool
Proven in 25+ years of use by organizations of all sizes. Eller s.r.o. is certified to ISO 9001:2015 and ISO/IEC 27001:2022